Press Space to continue
Supply chain attack prevention approaches and tradeoffs
Press Space to continue
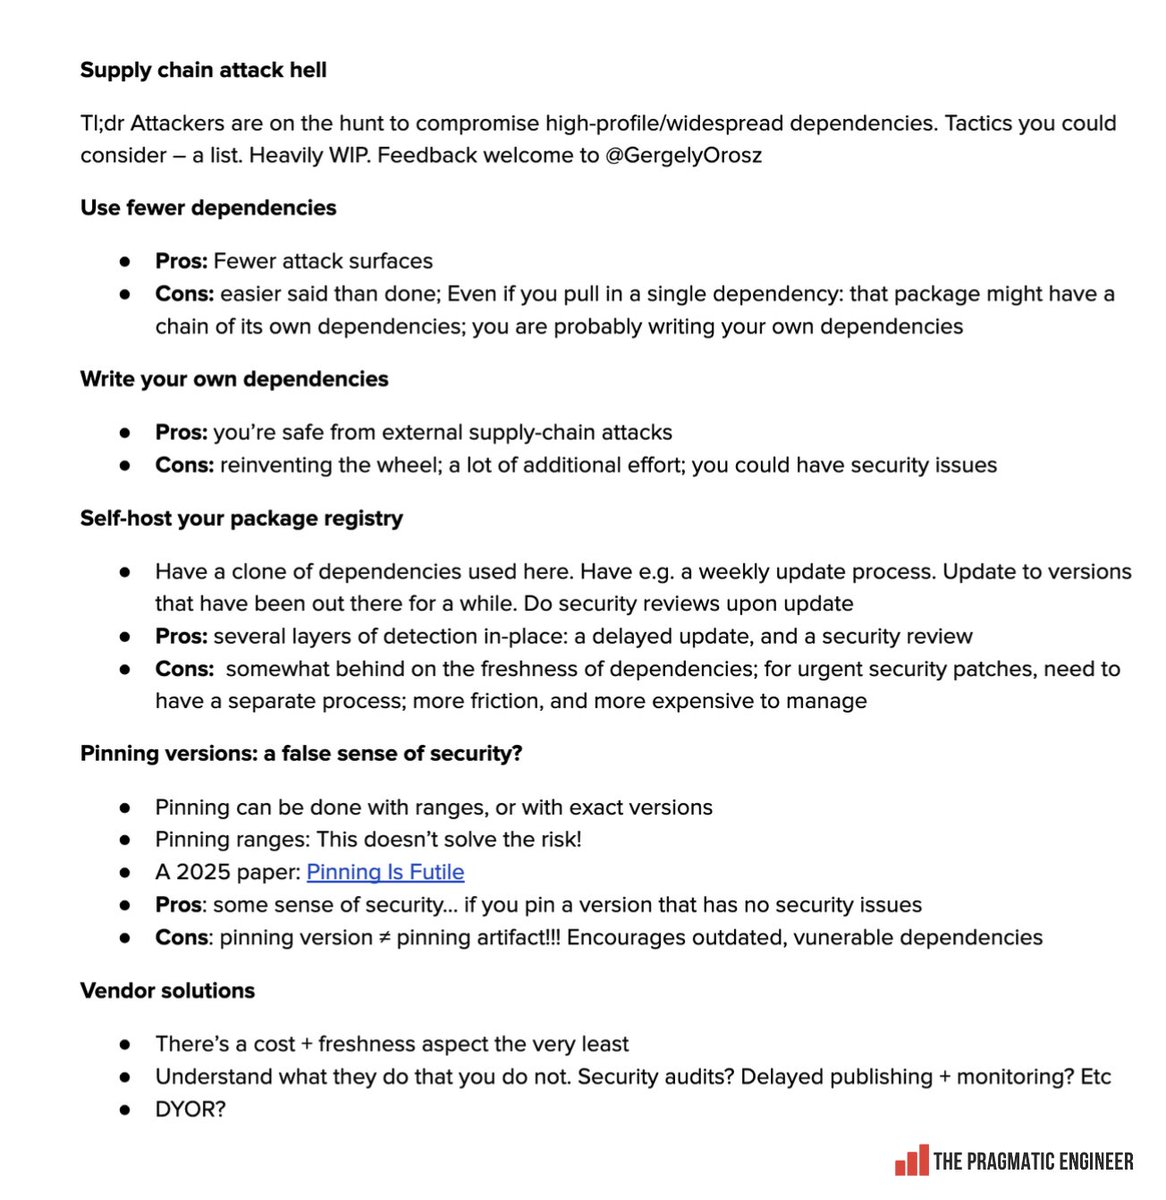
Supply chain attacks are happening left and right with npm, PyPI and so many other places. It seems to be getting worse, everyone agrees. But what can you do about it? Some thoughts on possible approaches (all have tradeoffs). What did I miss? And what vendors actually work?
open on x · 3 viewsViews and clicks count once per visitor per day. Clicks are opens of this post on X.